Unpacking Hidden Data: Digital Forensics with Binwalk & Magic Bytes
Firmware Analysis- Binwalk
Deep Dive
Data is compiled from public records and verified media reports.
Last Updated: October 30, 2026
Final Thoughts
For 2026, Bitmap Binwalk remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
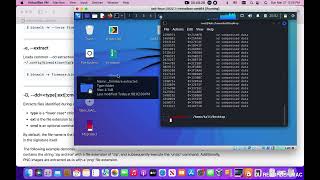
Demonstration of LSB algorithm reverse engineered with In this video, we use the powerful Kali Linux tool In this CTFlearn video, we do a writeup of the Welcome to 4DeepLearn! Aaj ke video mein hum seekhenge ** In this video, we walk through the "EXIF - Thumbnail" steganography challenge on Root-Me. Watch how we analyze a seemingly ... Mehrnaz N demonstrates how to recover and extract hidden files from a firmware image using Binwalk and the DD command. The process involves identifying file signatures and calculating offsets to carve out specific data chunks without specialized extraction tools. This video has a page on 0DE5 with exercises and resources ... Ever wondered how forensic investigators uncover hidden files and detect disguised malware? In this video, we dive deep into file ... This video explains how to perform firmware analysis using a tool called