Looking for the latest information on Trickbot Base64 Deobfuscation? We've compiled comprehensive data, records, and insights about Trickbot Base64 Deobfuscation.
Important Facts
Explore the primary sources for Trickbot Base64 Deobfuscation.
Recent Updates
Stay updated on Trickbot Base64 Deobfuscation's latest milestones.
Obfuscated Maldoc: Reversed BASE64
base64.decode(aW5uZHkudHcgW2F0XSBnbWFpbC5jb20K)
[11/10/2020] Emotet Maldoc Analysis - Embedded DLL and CertUtil for Base64 Decoding
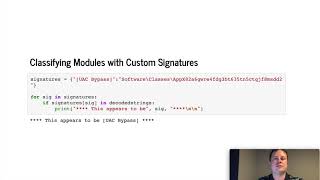
Decoding Obfuscated BASE64 Statistically
Turning Trickbot: decoding an encrypted command-and-control channel
Analysing Obfuscated VBA - Extracting indicators from a Trickbot downloader
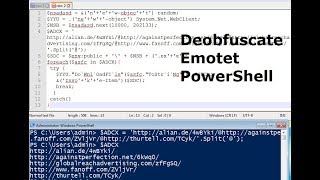
Deobfuscate Emotet PowerShell
Unpacking and Extracting TrickBot Malware Configuration With x64dbg and Python
API Deobfuscator: Resolving Obfuscated API Functions In Modern Packers
Emotet Malware Analysis - Part 2 - Deobfuscating PowerShell
TrickBot malware now checks screen resolution to evade analysis !!! | ICSS NewsRoom
Expert Insights
Data is compiled from public records and verified media reports.
Last Updated: October 31, 2026
Final Thoughts
For 2026, Trickbot Base64 Deobfuscation remains one of the most talked-about information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
Featured sample: beta.virusbay.io/sample/browse/0a7da84873f2a4fe0fcc58c88bbbe39d Source code of the utility: ... A single JavaScript file arrives as an email attachment. It looks gibberish — thousands of characters of obfuscated code that ... Sample: virustotal.com/en/file/2ebeef906142f328168e7e62e8be7fbaee48e3521853d76ea778005ada6e938a/analysis/ ... More info: videos.didierstevens.com/2021/11/23/obfuscated-maldoc-reversed- Earlier today (11/10/2020), AnyRun posted an Emotet maldoc that utilized CertUtil to decode a DLL payload that was used for ... This presentation by Andrew Brandt (Symantec) was presented at VB2017 in Madrid, Spain. A rather lengthy video to showcase my analysis techniques and thought processes when analysing malicious macros. In this case ... securityinbits.com/malware-analysis/ by Seokwoo Choi Modern packers use API obfuscation techniques to obstruct malware sandboxes and reverse engineers. In this and the next video we'll analyse a sample from the popular Emotet malware. Very well-known by now, with its own ... Indian Cyber Security Solutions - News Room presents daily news on cybersecurity. Today's (2nd July 2020) news: The infamous ...